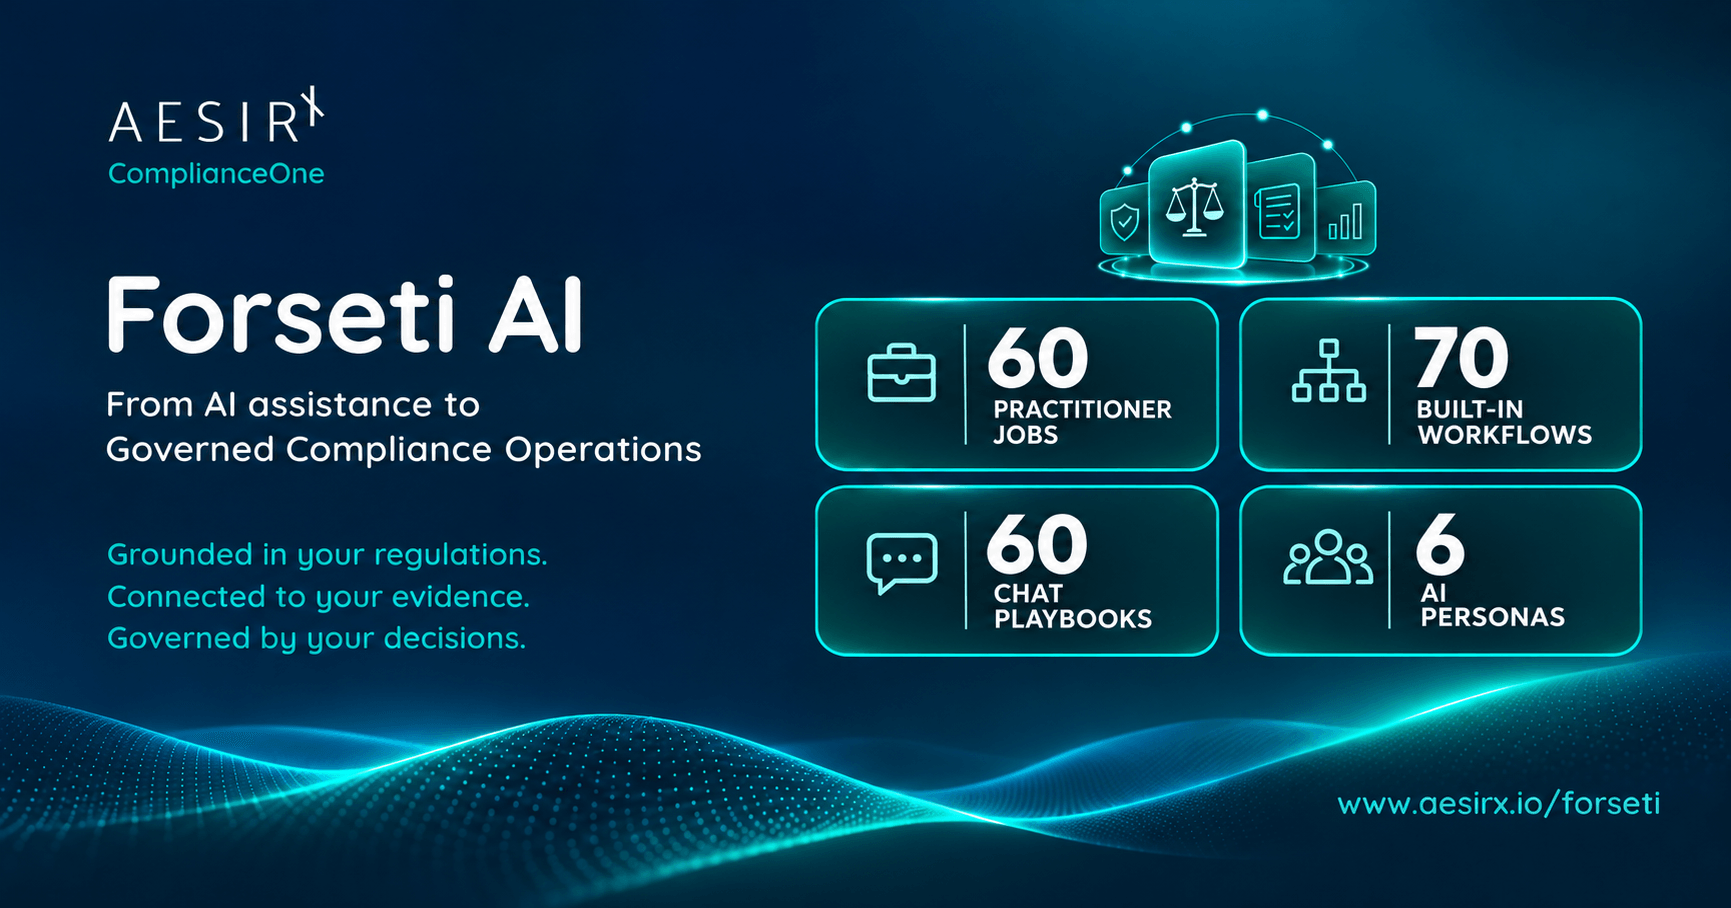
TL;DR: AesirX announces a major expansion of Forseti AI, introducing 60 compliance practitioner jobs, 70 built-in AI workflows, 60 specialist playbooks, advanced document review, delegated AI research, and a more powerful agentic execution environment within ComplianceOne.
Beyond AI That Answers Questions
Artificial intelligence has demonstrated its ability to summarize documents, answer questions, generate content, and assist with research.
But for organizations operating in regulated environments, answering a question is rarely the end of the work.
A Data Protection Officer needs to assess whether a processing activity requires a DPIA, examine the supporting records, identify missing evidence, prepare the assessment, and document the resulting decisions.
A compliance manager needs to identify applicable obligations, evaluate existing controls, prepare remediation activities, assign accountability, and demonstrate progress.
An internal auditor needs to define an audit scope, select evidence, assess findings, prepare corrective actions, and preserve a defensible record of the review.
These activities require more than a capable language model.
They require access to the right organizational context, applicable regulatory requirements, structured processes, evidence, permissions, and accountable human decisions.
This is the problem Forseti AI was designed to solve.
Today, AesirX is announcing a major expansion of Forseti AI, transforming its role inside ComplianceOne from an auditable AI assistant into a comprehensive environment for governed, AI-assisted compliance operations.
The Forseti AI Upgrade
The expansion covers privacy, legal, risk, governance, internal audit, AI governance, business continuity, third-party management, and operational compliance.
Most importantly, these capabilities operate within the existing ComplianceOne architecture, using the organization's own records, permissions, and installed regulatory frameworks.
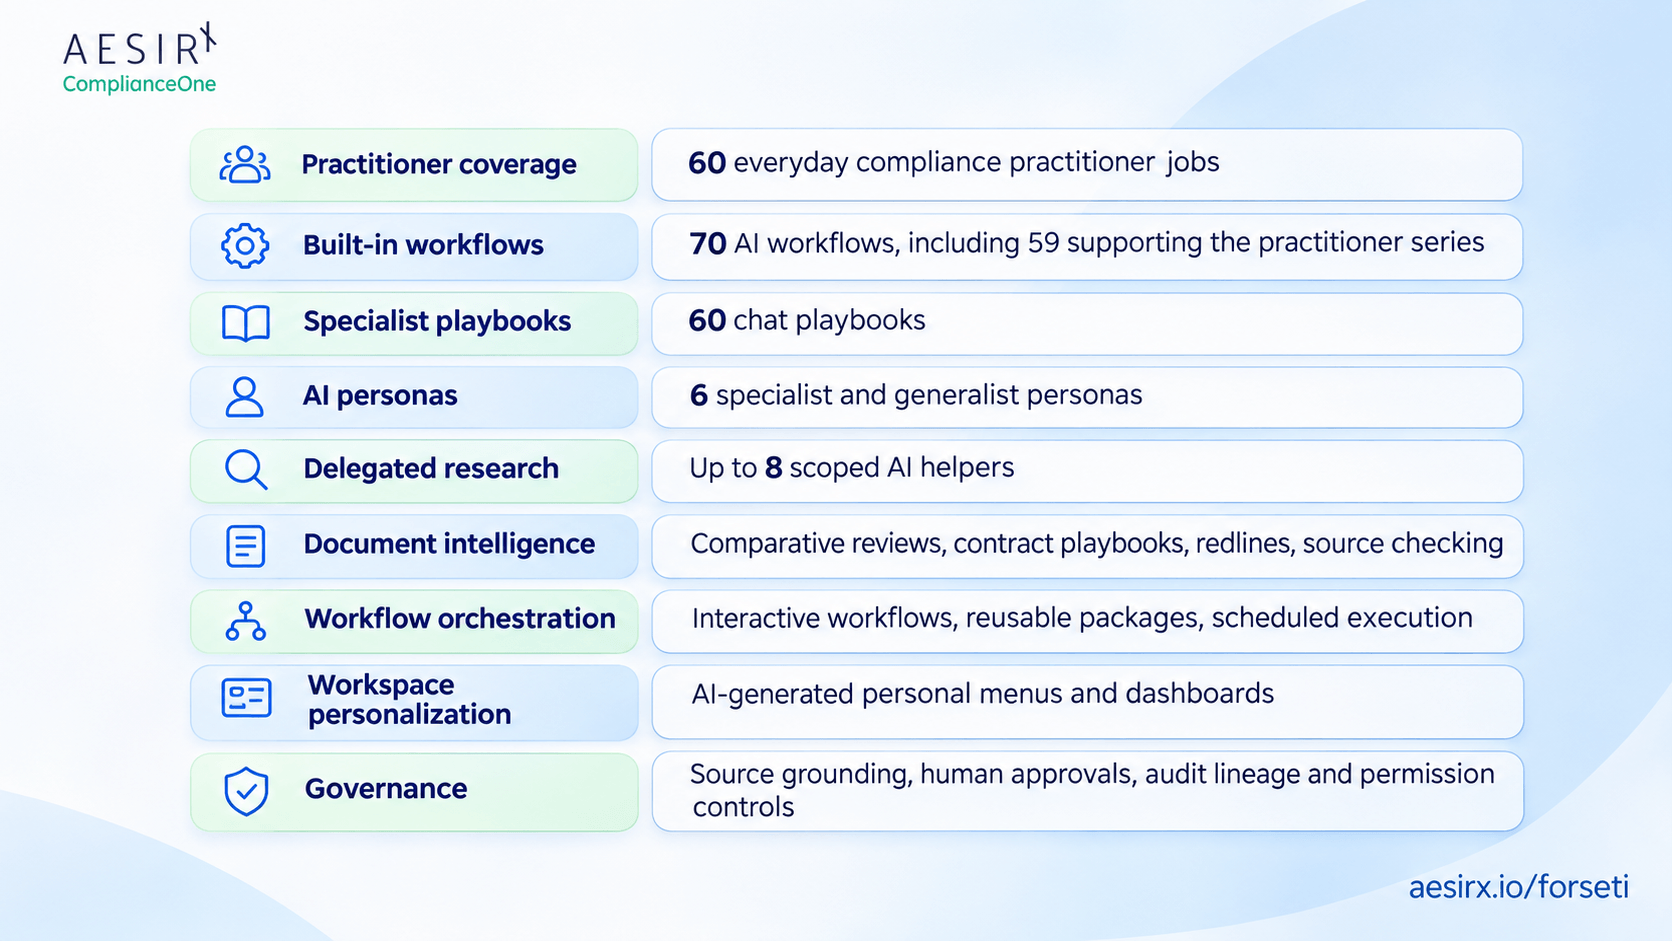
1. Introducing 60 Practitioner Jobs
The foundation of the upgrade is the Forseti AI Practitioner Series.
It introduces 60 structured practitioner jobs, supported by 59 workflows, including 54 new workflows and five rebuilt capabilities.
These are not generic prompt templates.
Each workflow is designed around a recognizable task performed by a compliance, legal, privacy, risk, or audit professional.
The workflows read relevant organizational records, apply available regulatory context, examine supporting evidence, and generate structured outputs for human review.
Privacy and Data Protection
Forseti supports practitioners working with GDPR, Vietnam's Personal Data Protection Law, and other activated privacy frameworks.
Capabilities include:
- DPIA and impact assessment screening against framework-specific requirements.
- Review of Records of Processing Activities for completeness and sufficiency.
- Privacy notice analysis against documented processing activities.
- Cross-border transfer risk assessments and supporting documentation.
- Data subject rights request preparation and review.
- Processor agreement analysis and subprocessor register checks.
- Identification of unsupported statements and missing evidence.
Rather than generating a generic assessment from a prompt, Forseti can work from the organization's actual processing records and identify where information, evidence, or decisions remain incomplete.
Risk Management and Governance
The expanded risk capabilities support the operational lifecycle of organizational risk management.
Forseti can prepare risk methodology drafts, generate an initial risk register from identifiable organizational records, develop treatment plans, review risk acceptance proposals, and examine risk-to-control traceability.
Risk assessments use the organization's own versioned methodology.
Risk scores, acceptance decisions, ownership, and approved changes remain governed by ComplianceOne's records and human decision processes.
The platform also supports Statements of Applicability for ISO/IEC 27001, ISO/IEC 27701, and ISO/IEC 42001, including control applicability, exclusions, evidence mapping, and approval workflows.
AI Governance
As organizations deploy AI systems across their operations, maintaining visibility and accountability becomes increasingly important.
Forseti now supports:
- AI system inventory completeness checks.
- Review of documented AI risk classifications.
- AI impact assessment preparation and review.
- AI supplier due diligence.
- Drafting of organizational AI use policies.
- AI management system scope preparation.
- Alignment with applicable requirements under ISO/IEC 42001 and installed AI regulatory frameworks.
These capabilities support organizations establishing a documented and evidence-based approach to AI governance, including the operational requirements introduced by emerging AI legislation.
Forseti identifies and explains potential gaps. It does not independently assign regulatory risk classifications or make binding governance decisions.
Internal Audit and Evidence Management
Forseti also expands the day-to-day capabilities available to internal auditors and compliance assurance teams.
Practitioners can prepare audit programmes, generate scope-specific checklists, select evidence samples using documented rules, prepare interview briefings, convert evidence requests into proposed tasks, and draft corrective actions.
Evidence workflows support freshness reviews, access review preparation, change evidence sampling, and logging and monitoring evidence packs.
The goal is to reduce repetitive preparation while strengthening the connection between audit conclusions and the records supporting them.
Incidents and Business Continuity
Incident response requires coordinated work under time pressure.
Forseti assists with incident triage, notification obligation reviews, post-incident analysis, response plan drafting, tabletop exercises, business impact assessments, and recovery test preparation.
It distinguishes documented root causes from contributing factors and uses recorded incident classifications and deadlines rather than inventing them.
Business impact analysis and restoration testing are connected to structured operational records, including calculated results where required.
Vendors and Third Parties
Forseti supports vendor risk assessments, questionnaire analysis, evidence-backed questionnaire responses, and third-party risk explanations.
Where an answer lacks sufficient evidence, Forseti identifies the missing source rather than presenting an unsupported claim as fact.
Enterprise capabilities also include ICT third-party register and risk framework checks where an activated framework requires them, including DORA.
2. From Chat to Agentic Workflows
Forseti's expanded capabilities go substantially beyond conversational AI.
Its workflow environment connects specialist skills, organizational context, regulatory knowledge, operational records, and controlled execution.
A practitioner can start with a question in Forseti Chat, receive relevant guidance, and move directly into a structured workflow for the task.
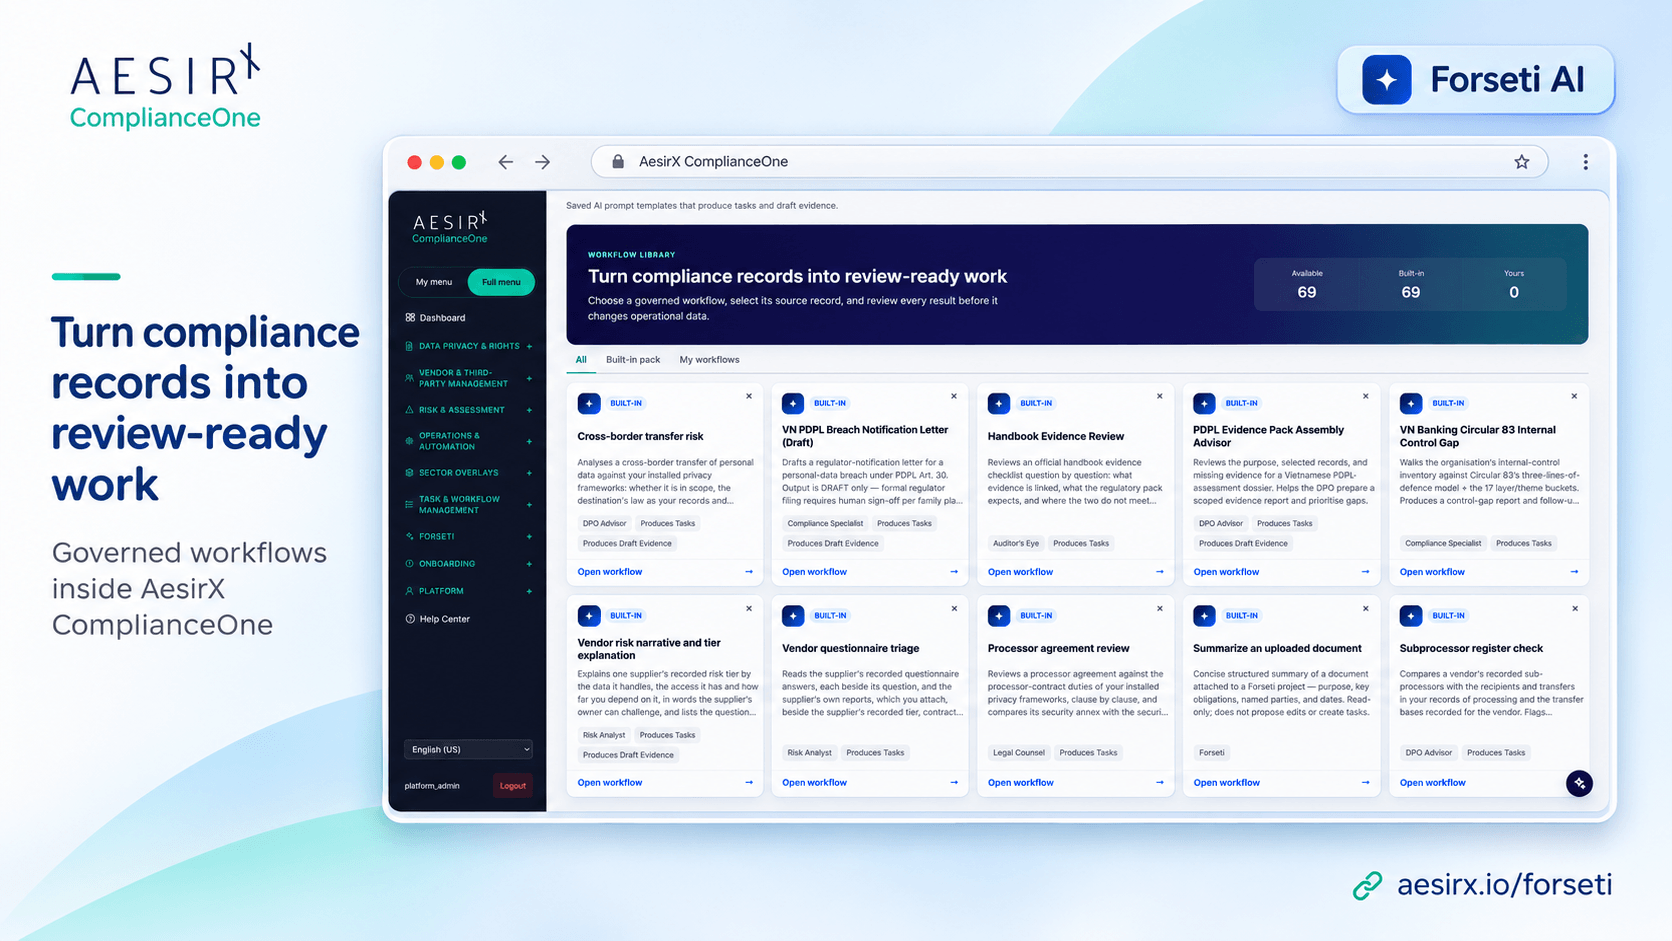
60 practitioner playbooks across six personas help connect the user's question to the appropriate operational process.
The six available personas are:
- Generalist
- Compliance Specialist
- Legal Counsel
- DPO Advisor
- Risk Analyst
- Auditor's Eye
Each persona operates within defined professional boundaries and applies the same requirements for source grounding, permissions, and human approvals.
The expanded workflow platform introduces additional capabilities.
Interactive workflows: A workflow can request specific additional information when it reaches a defined decision point instead of making unsupported assumptions.
Delegated research: Forseti can coordinate up to eight scoped AI helpers for research tasks, with the work remaining within defined permissions and review boundaries.
Reusable workflow packages: Workflows can be exported and imported, making it easier to standardize approved processes across appropriate organizational environments.
Scheduled execution: Supported workflows can operate on recurring schedules, including monthly, quarterly, or annual review cycles.
Audit lineage: The platform records the relationship between AI activity, tools, records, sources, proposed changes, and human decisions.
This creates a foundation for AI-supported operational work that is repeatable, inspectable, and governed.
3. Advanced Document Intelligence and Legal Review
Document-heavy work represents a substantial part of compliance and legal operations.
The upgrade extends Forseti's existing document review capabilities with deeper comparative analysis and structured contract review.
Contract Playbooks and Controlled Redlines
Organizations can maintain versioned contracting positions and review agreements against those positions.
Forseti can identify relevant contractual provisions, compare them with documented requirements, and prepare suggested changes for review.
The expanded document environment includes tracked-change redlines, document previews, full-text search, and upload validation.
Changes remain proposed edits until an authorized reviewer accepts them.
Comparative Document Analysis
Forseti supports side-by-side reviews of agreements, privacy notices, policies, transfer documentation, and other supported documents.
Tabular reviews allow users to compare multiple documents against selected criteria.
For example, a legal team could compare vendor contracts across governing law, termination, liability limitations, indemnification, data processing requirements, and contractual obligations.
Source references connect the extracted findings back to the relevant documents.
Verified Source References
The expanded source-verification capabilities check extracted quotations against their supporting material and distinguish exact matches from quotations that cannot be verified.
This helps reviewers identify where further inspection is needed before relying on or distributing an AI-generated work product.
Source verification does not replace professional review, but it provides another important control against unsupported output.
Support for Law Firms
These capabilities also complement AesirX ComplianceOne for Law Firms, where Forseti supports permitted client-matter research, drafting, document review, and preparation of legal work products.
Client intake, matter context, legal research, review, and client delivery remain connected through controlled records and professional sign-off.
4. AI That Understands the Organization
A critical difference between a generic AI assistant and Forseti is the context in which the work takes place.
Forseti is integrated with ComplianceOne's operational environment.
It can use relevant organizational information, such as processing activities, assessments, vendor records, risks, controls, policies, incidents, and evidence, subject to the current user's permissions.
It also uses the regulatory frameworks the organization has explicitly installed and activated.
This matters because compliance is not performed against an abstract collection of laws.
It is performed against specific obligations that apply to a particular organization, its activities, its risk profile, and the evidence available at a particular point in time.
Regulatory Framework Grounding
AesirX ComplianceOne supports more than 175 regulatory frameworks and standards across multiple jurisdictions and industries.
Forseti uses the relevant installed framework content rather than treating general model knowledge as authoritative regulatory evidence.
This includes supported requirements from frameworks such as:
- Vietnam's Personal Data Protection Law and implementing regulations.
- GDPR and relevant European regulatory requirements.
- DORA for applicable financial-sector organizations.
- Vietnam's AI regulatory framework.
- ISO/IEC 27001, ISO/IEC 27701, and ISO/IEC 42001.
- SOC 2-related governance and assurance requirements.
- Applicable industry and sector-specific regulatory overlays.
Framework availability and workflow applicability depend on the organization's installation, configuration, and regulatory scope.
AesirX provides operational support for standards-based compliance work; it does not issue certifications or replace independent certification bodies.
Organizational Memory
Forseti also supports organization-scoped memory for relevant prior interpretations, documented preferences, risk positions, and unresolved compliance matters.
This allows organizational context to inform future work without treating an earlier AI-generated answer as an automatically approved decision.
The objective is to help organizations develop continuity in their governance processes while preserving appropriate review and authority.
5. A Personal Compliance Workspace, Built with AI
The upgrade also changes how users interact with ComplianceOne itself.
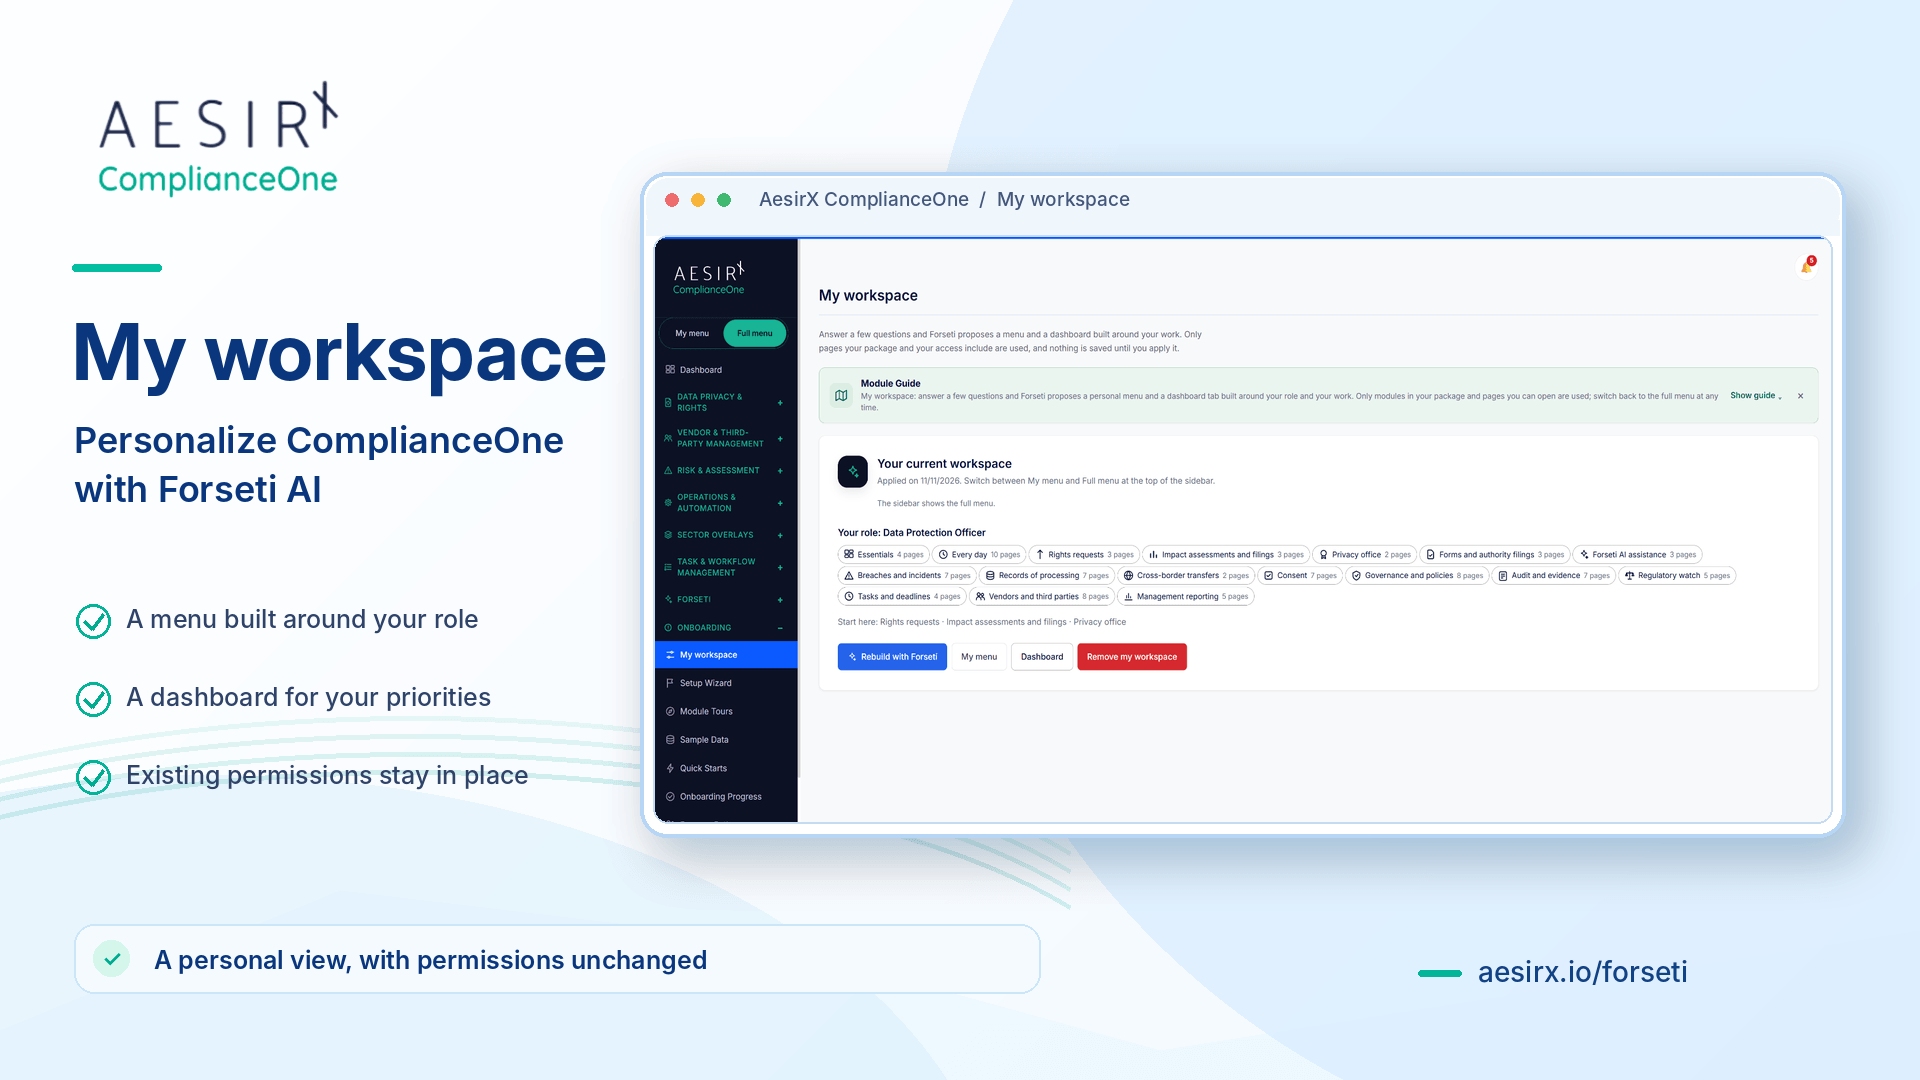
With Forseti's personalized workspace capability, users can describe their role, responsibilities, and priorities through a guided process.
Forseti then proposes a personalized navigation menu and dashboard.
For example, a Data Protection Officer may prioritize processing activities, impact assessments, transfers, and rights requests.
A risk manager may focus on risk registers, treatment activities, control ownership, and reporting.
An internal auditor may prioritize audit programmes, evidence, findings, and corrective actions.
Users can review, adjust, and apply their proposed workspace configuration.
Personalization changes how information is presented. It does not change the user's underlying permissions or grant access to restricted records.
The result is a more relevant daily working environment built around the responsibilities of each practitioner.
6. Designed for Human Accountability
More capable AI systems need stronger operational controls, not fewer.
This principle remains fundamental to Forseti.
Forseti prepares work. Authorized people make decisions.
The expanded practitioner workflows produce structured findings and identify four important categories:
Not checked: What the workflow did not examine or could not establish.
Decisions for you: What requires an authorized person's judgment or approval.
Questions: What additional information is required.
Re-check when: What events or changes should trigger another review.
These outputs make limitations and outstanding responsibilities visible rather than allowing an apparently complete AI response to conceal uncertainty.
Forseti does not independently approve evidence, accept risks, finalize risk classifications, authorize record changes, close audit findings, or submit regulatory filings.
Human review and approval remain part of the operating process.
Every relevant action is connected to ComplianceOne's audit lineage, creating a traceable record of what the AI used, proposed, and produced, and what an authorized person subsequently decided.
A generated output is not automatically an approved compliance record, and running an AI workflow does not establish that an organization is compliant.
7. Self-Hosted Infrastructure and Bring Your Own Keys
Forseti operates within the broader ComplianceOne architecture, where customer control over infrastructure, information, and AI services is a core design principle.
ComplianceOne is deployed as customer-managed, self-hosted software.
Customers can operate the platform on infrastructure under their control and configure supported AI models through a Bring Your Own Keys (BYOK) approach.
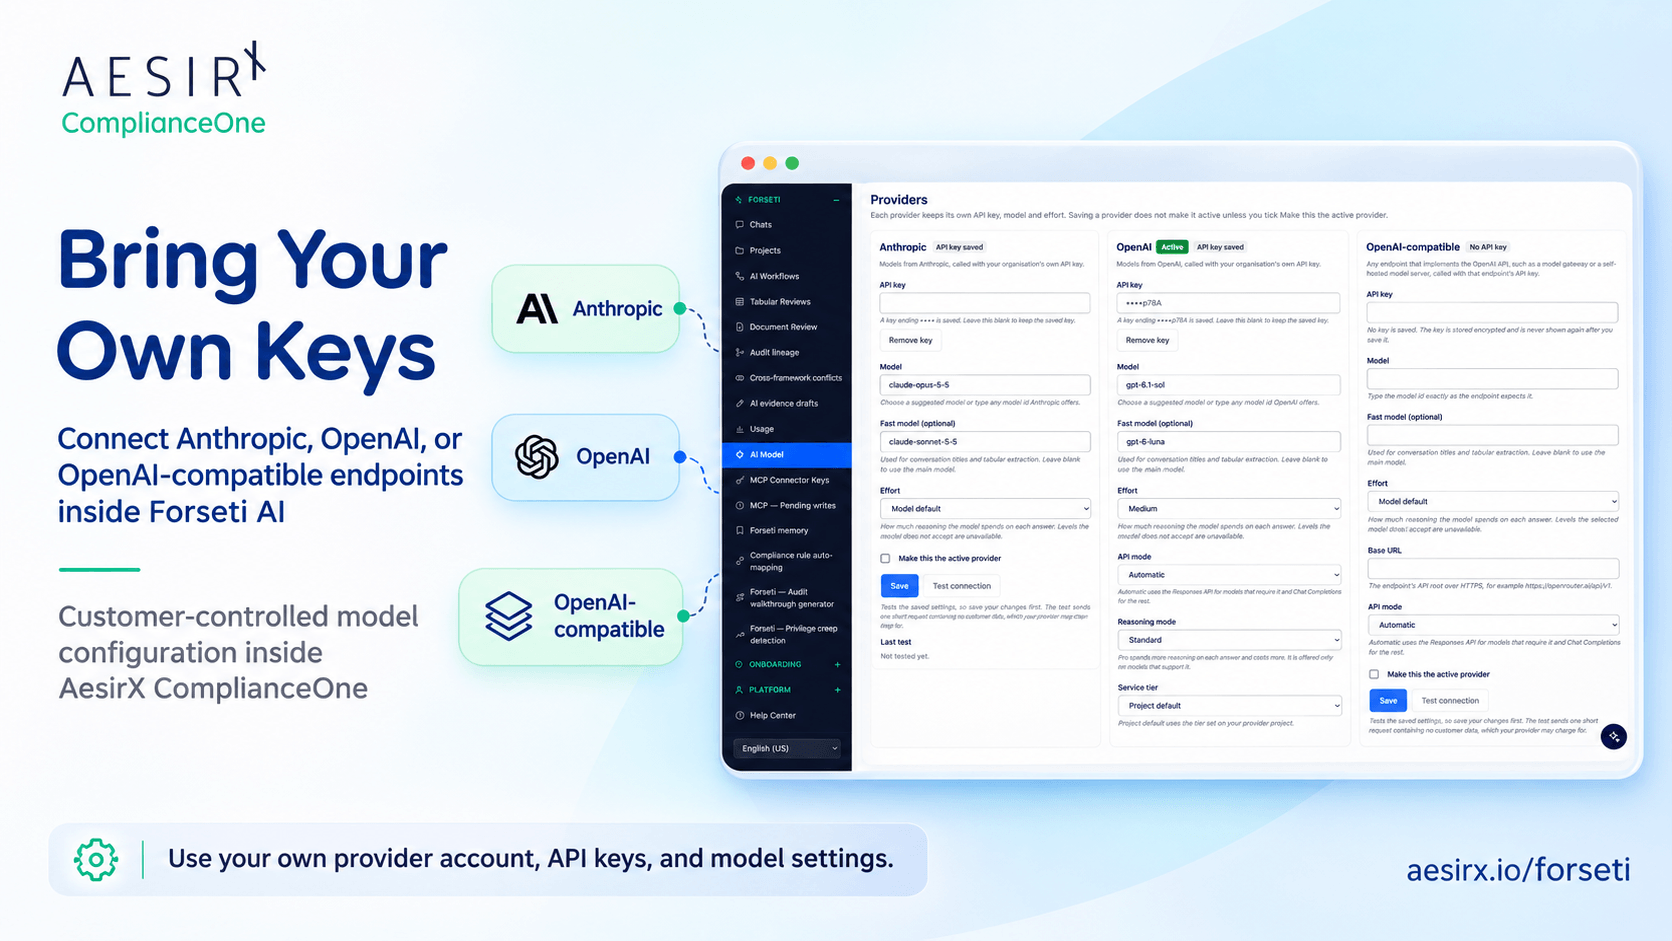
This gives organizations flexibility to choose among supported providers and compatible model options, including commercial AI services and appropriately configured self-hosted or sovereign models.
The selected AI model is not the product's defining dependency.
The value is in the operational framework surrounding the model: regulatory knowledge, organizational context, permissions, workflows, evidence, validation, and auditability.
Customers maintain their own AI-provider relationships and must assess the processing, retention, location, and contractual conditions associated with their chosen model services.
AesirX supplies the software and agentic operating environment. It does not require access to customer operational data in customer-managed deployments.
This separation allows organizations to evaluate AI services according to their security, data protection, operational, and commercial requirements.
8. Bringing Forseti into Existing AI Environments
Forseti is not limited to interactions within the ComplianceOne interface.
Its Model Context Protocol (MCP) connector allows compatible external AI clients and integrations to access a controlled set of Forseti capabilities.
Organizations can provide scoped access to selected tools for activities such as regulatory research, document retrieval, and preparation of proposed operational changes.
API keys and tool permissions determine which capabilities an integration can access.
External write operations do not bypass ComplianceOne's approval process.
Proposed changes are reviewed within the platform before authorized execution.
This makes it possible to integrate Forseti into broader AI-assisted working environments without sacrificing the underlying governance model.
9. An Operational Foundation That Extends Beyond Individual Workflows
The expanded practitioner capabilities build on ComplianceOne's broader regulatory operations platform.
With 30 integrated modules, including Sector Overlays, ComplianceOne connects regulatory obligations to operational records, assessments, controls, evidence, incidents, tasks, approvals, and governance processes.
Forseti provides an AI-assisted operating layer across those capabilities.
That means its value is not limited to generating a report or completing a single assessment.
It can support connected activities across the compliance lifecycle.
Consider an organization introducing a new AI-enabled service.
Its teams may need to document the processing activities, evaluate privacy obligations, assess the AI system's risk classification, review relevant vendors, identify controls, prepare policies, and collect supporting evidence.
These are different responsibilities, often involving different professionals.
Forseti can assist with multiple stages while keeping each task connected to the appropriate organizational records and applicable regulatory requirements.
The same principle applies to preparing an internal audit, reviewing a supplier, responding to an incident, or establishing a new management system.
The objective is not isolated AI productivity.
It is coordinated compliance work with traceable evidence and accountable decisions.
10. The Next Step in Agentic Regulatory Technology
Many AI products can generate an answer.
Fewer are designed to connect that answer to the organization's own records, applicable regulations, authorized workflows, evidence, and approval processes.
That distinction is increasingly important as organizations evaluate how far AI can responsibly participate in regulated operations.
At AesirX, our approach is built on three principles:
Context before generation. AI must work with the relevant organizational and regulatory context, and make missing information visible.
Governed execution before autonomy. AI should help complete meaningful operational work without bypassing professional responsibility, permissions, or approval controls.
Evidence before assertion. Findings and proposed actions should be traceable to their supporting sources and recorded decisions.
The expanded Forseti AI capabilities bring these principles together across a much larger range of practitioner activities.
We are not building AI to replace Data Protection Officers, lawyers, compliance managers, risk professionals, or auditors.
We are building AI that helps these professionals complete more of the operational work required of them, while preserving the judgment, accountability, and evidence that regulated organizations depend on.
The future of compliance AI is not simply better answers.
It is better-governed work.
Ronni K. Gothard Christiansen
Technical Privacy Engineer and CEO, AesirX.io
Explore the New Forseti AI
Forseti AI is available as part of the AesirX ComplianceOne product family, with capabilities and workflow availability determined by the relevant product edition and configuration.
Organizations evaluating Forseti can explore the practitioner workflows, regulatory grounding, document intelligence, human approval processes, and customer-controlled deployment options.
Discover how Forseti can support your organization's compliance, privacy, legal, risk, and audit operations.
Explore Forseti AI: https://aesirx.io/forseti
About AesirX
AesirX develops privacy-first technology and regulatory compliance software designed to help organizations manage data protection, governance, risk, and regulatory obligations.
Its flagship ComplianceOne platform combines 30 operational modules, regulatory framework support, sector-specific capabilities, and Forseti AI to connect regulatory obligations with organizational evidence, workflows, and accountable decisions.
AesirX emphasizes customer-controlled infrastructure, privacy engineering, model flexibility, and governance by design.
Website: https://aesirx.io
Forseti AI: https://aesirx.io/forseti
Frequently Asked Questions About the Forseti AI Upgrade
It helps compliance, legal, privacy, risk, and audit professionals perform structured tasks while maintaining source traceability, permissions, human oversight, and audit records. Its purpose is not simply to generate information but to support governed compliance operations.
New capabilities include advanced privacy assessments, risk management workflows, AI governance reviews, internal audit preparation, contract analysis, tracked-change redlines, source-verified outputs, and delegated research using up to eight scoped AI helpers.
The upgrade also introduces interactive workflows, reusable workflow packages, expanded organizational record access, and AI-powered workspace personalization.
AI personas provide role-specific assistance for professionals such as compliance managers, legal counsel, Data Protection Officers, risk analysts, and auditors.
Chat playbooks guide Forseti's responses to common practitioner questions and help users identify relevant processes.
AI workflows execute structured tasks against organizational records and applicable frameworks, producing findings, assessments, drafts, or proposed actions for human review.
Together, they connect conversational assistance with practical compliance work.
Workflow findings identify supporting sources and distinguish verified information from missing or unassessed material.
The expanded document review capabilities also support quotation verification against original source material.
This reduces reliance on unsupported model-generated assertions, while preserving the need for professional review and interpretation.
It can analyze evidence, prepare assessments, draft documents, identify gaps, and propose actions. However, it does not independently approve records, accept risks, establish binding risk classifications, close audit findings, or submit regulatory filings.
Proposed changes require authorized human review and application. Relevant actions and decisions remain traceable through ComplianceOne's audit lineage.
Running an AI workflow does not, by itself, establish regulatory compliance.
Forseti applies the framework content that the customer has explicitly installed and activated. The availability of individual workflows depends on the applicable framework, organizational configuration, and product edition.
Organizations can review agreements against versioned contracting positions, compare documents against defined criteria, identify missing or inconsistent provisions, and prepare tracked-change redlines.
Additional capabilities include document previews, full-text search, and source-verified quotations.
These features also support AesirX ComplianceOne for Law Firms, where legal professionals can use Forseti to assist with research, drafting, document review, and client-matter workflows while retaining professional responsibility for the final work product.
Through Bring Your Own Keys (BYOK), organizations can configure supported commercial AI providers, compatible models, or appropriately deployed self-hosted and sovereign AI models.
Customers retain control over their ComplianceOne infrastructure and their AI-provider relationships. AesirX does not require access to customer operational data in self-hosted deployments.
Where external AI providers are selected, the organization's arrangements with those providers determine the applicable data processing, retention, and hosting conditions.
Authorized integrations can access selected capabilities for regulatory research, information retrieval, and preparation of proposed operational actions.
Access is governed by configured permissions, and external integrations cannot bypass the platform's human approval requirements for protected operations.
Forseti also supports reusable workflow packages and scheduled execution, helping organizations standardize recurring compliance activities.
Through a guided questionnaire, Forseti proposes a workspace configuration that users can review, modify, and apply.
For example, a Data Protection Officer can prioritize privacy assessments and processing records, while an internal auditor can focus on audit programmes, evidence, findings, and corrective actions.
Workspace personalization changes the presentation of available functions without modifying permissions or granting additional access.
Learn more about Forseti AI: https://aesirx.io/forseti


