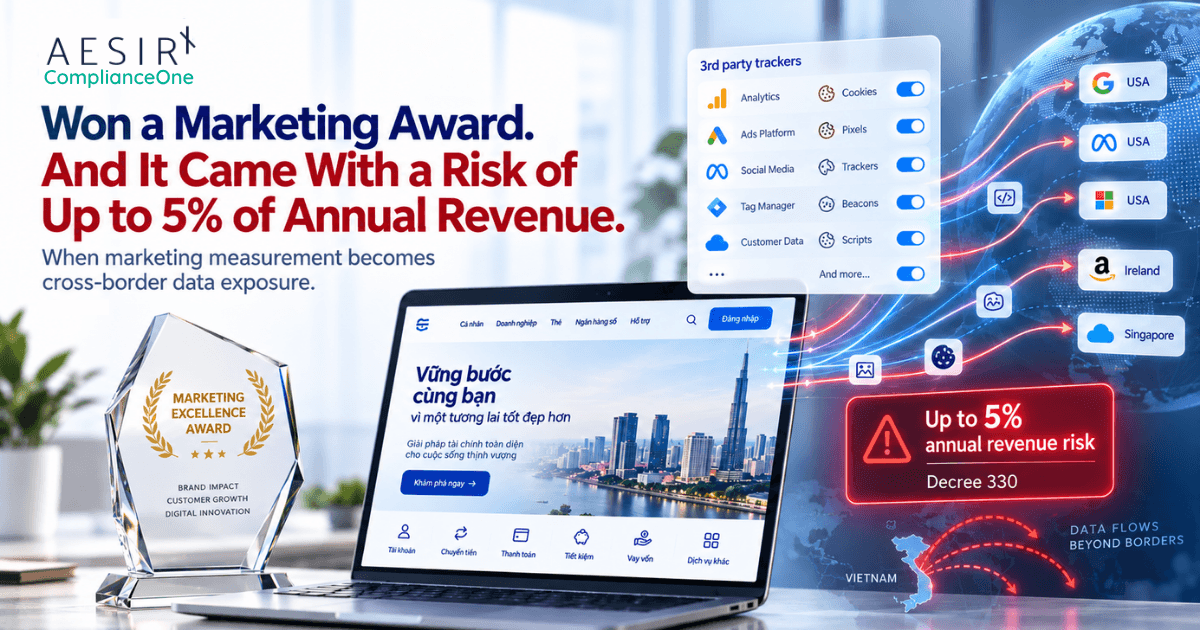
TL;DR: I saw a major Vietnamese bank proudly celebrating a marketing award. When I inspected its public website, I found 48 third-party cookies and tracking beacons, including connections involving Google, Meta, TikTok and other external infrastructure, with several activating before the visitor had made a consent choice. Under Vietnam’s 2026 regulatory environment, that is a serious governance issue: behavioural tracking is classified as sensitive personal data, behavioural and targeted advertising based on website tracking requires consent, cross-border transfers carry their own evidence obligations, and Decree 330 now puts specified cross-border personal-data violations inside a penalty regime that can reach 5% of prior-year revenue.
I saw one of Vietnam’s large banks celebrating a marketing award. The marketing team posted about it, the marketing director posted about it, and agencies and suppliers involved in the work joined in. There were photographs, congratulations and plenty of pride in what had clearly been a successful campaign.
Then I opened the bank’s website and looked at what the browser was actually doing.
Our technical review detected 48 third-party cookies and tracking beacons, with connections involving Google, Meta, TikTok and other third-party infrastructure. Several were active before the visitor had made a meaningful consent choice.
That contrast is what stayed with me. The marketing success was highly visible. The underlying data flows were almost invisible unless somebody actually inspected the network traffic.
“The marketing team was measuring the customer. Who was measuring the marketing stack?”
The browser was telling a different story
To the customer, a bank website looks entirely first-party. There is the bank’s domain, its logo, its products, its privacy notice and its customer journey. Underneath that interface, however, the browser can be communicating with a much larger ecosystem of advertising, analytics, attribution, social-media and optimisation providers.
Those connections matter because modern marketing measurement is data processing. A browser request can carry identifiers, page context, timestamps, device and browser information, IP-derived information, campaign parameters and behavioural events. Depending on the implementation, further information can be added through tag managers, forms, account states, conversion events or server-side integrations.
Vietnam’s regulatory environment now puts that behaviour into a very different category. Article 4 of Decree 356 expressly includes data tracking behaviour and the use of telecommunications, social networks, online media and other cyberspace services in the sensitive-personal-data list. It separately includes specified banking, financial, credit and transaction information.
For a bank, marketing technology therefore operates inside an unusually sensitive data environment. The key question is no longer whether a particular script is called analytics, advertising, attribution or a cookie. The important question is what data is processed, where it goes, why it goes there and who is accountable for the decision.
Consent has become a technical control
Vietnam’s Personal Data Protection Law 91/2025/QH15 and Decree 356/2025/NĐ-CP have both been effective since 1 January 2026.
That turns consent into an engineering issue as much as a legal one. When consent is required for a particular marketing or behavioural-processing activity, the relevant technology has to respect that choice in the order in which the browser executes it. If a tracker or advertising endpoint receives data as the page loads, the processing has already started.
A privacy notice can describe the intended model and a consent interface can present the visitor with a choice. The network traffic shows whether the technical implementation actually followed that choice.
“A consent banner is a user interface. The network request is evidence of what the website actually did.”
This is where large organizations can develop a dangerous gap between teams. Legal reviews the wording, Marketing reviews campaign performance, agencies configure tags, developers implement the site, Procurement handles contracts, and Privacy manages assessments and governance. Each function sees part of the environment while the visitor’s browser executes all of their decisions together.
Decree 330 changed the financial stakes
On 19 August 2026, Decree 330/2026/NĐ-CP entered into force, creating Vietnam’s current administrative-penalty framework for cybersecurity and personal-data protection.
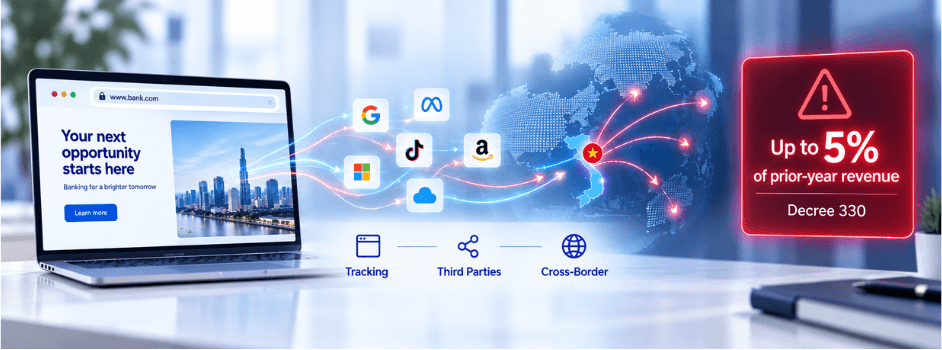
For personal-data protection violations, the maximum organizational penalty for other violations can reach VND 3 billion. For unlawful buying or selling of personal data, the maximum can reach ten times the proceeds obtained from the violation. Most importantly for international digital infrastructure, the maximum penalty for an organization violating the cross-border personal-data-transfer rules can reach 5% of its prior-year revenue.
Decree 330 then applies revenue-based bands to specified serious cross-border violations. Article 8 provides a 3%–5% revenue range where qualifying conduct results in the leakage or loss of personal data concerning at least one million Vietnamese data subjects, as well as a specified route involving continued transfers after an authority has ordered them stopped.
For a major bank, percentages of annual revenue are no longer website-team numbers. They belong in enterprise risk.
“At 5% of annual revenue, an unmanaged marketing data flow stops being a website problem and becomes an enterprise-risk problem.”
The practical consequence is straightforward. Management needs to know what is leaving the bank’s controlled environment before it can govern the resulting exposure: which vendors receive the data, what categories are involved, which purpose applies, which systems initiate the transfer, what consent evidence exists, which cross-border assessment covers the recipient, who approved the configuration and when it was last technically verified.
Without those answers, the organization is relying on the marketing stack behaving as everyone assumes it behaves.
The cross-border issue extends far beyond the consent banner
Third-party marketing infrastructure is often international by design. Google, Meta, TikTok and similar providers operate global technology environments, and a website integration can create international data flows even when the internal business description is simply “analytics”, “conversion measurement” or “campaign optimisation”.
That makes the governance record just as important as the consent interface. A mature organization should be able to trace a material marketing technology from the webpage into the wider compliance model: the processing activity, data categories, purpose, vendor, recipient, consent mechanism, transfer assessment, responsible owner, technical implementation and evidence that the approved controls remain in place.
That evidence also has to survive routine digital change. Marketing changes agencies. A developer adds a new tag. A campaign introduces a different conversion tool. Google Tag Manager is updated. A new landing page goes live. The regulatory position cannot depend on somebody reconstructing the history six months later from emails and screenshots.
The evidence should be created as part of the change itself.
Scale brings the Data Law into the conversation
The Data Law adds another layer for large organizations. Decree 165/2025/NĐ-CP has applied since 1 July 2025 as the principal implementing decree under the Data Law, and Decision 20/2025/QĐ-TTg establishes the official lists of important and core data.
For a large financial institution, the consequence is that data category and scale must be understood rather than assumed. The organization needs an actual inventory showing which datasets exist, what they contain, how many data subjects they concern, where they are processed and which external systems receive them.
That analysis belongs alongside privacy and cross-border governance. Public-facing marketing technology should not be assumed to be low-risk merely because it sits on a public website. The page can still generate behavioural information, identifiers and signals that become regulated processing when combined with the actual implementation.
The technical facts come first. The legal mapping follows them.
This was not an isolated pattern
The bank stood out because of the contradiction between the public celebration and what the browser was quietly doing. But the underlying technical pattern is widespread.
Earlier this year, AesirX scanned 500 major Vietnamese corporate websites. Of the 340 websites that returned sufficient technical evidence for analysis, 244 — 71.8% — were classified as high technical risk, 273 — 80.3% — loaded tracking beacons, and 203 — 59.7% — loaded third-party cookies. Only 63 of the analyzed sites had neither detected during the scan, while Google Tag Manager appeared on 65% of them.
Those figures are technical observations, not regulatory findings. Their importance is that they show how deeply third-party infrastructure is embedded across major Vietnamese corporate websites.
The typical corporate website presents itself as a first-party environment while the browser may be communicating with several external providers before the visitor understands that those relationships exist.
“The privacy policy describes what the organization says. The browser shows what the organization does.”
That makes the corporate website an unusually transparent audit surface. An auditor does not need database access to inspect the first layer of behaviour. A regulator does not need the marketing team to list every pixel before checking what the page actually calls. Any technically competent reviewer can observe scripts, endpoints, timing and third-party requests from the browser itself.
What used to be hidden inside marketing implementation is increasingly externally testable.
Marketing technology is now data infrastructure
Many organizations still govern MarTech as a collection of campaign tools. That no longer reflects what the technology actually does.
Marketing systems identify browsers, measure behaviour, create audiences, connect sessions, record conversions, exchange identifiers, support retargeting and send events into external platforms. Tag managers make new processing easier to deploy, while server-side integrations can move part of that processing away from the browser without removing the governance requirement.
At enterprise scale, this is data infrastructure. It deserves the same discipline applied to other systems handling regulated information: an inventory of vendors and processing, named owners, documented purposes, data categories, transfer relationships, change control, technical testing and evidence.
Marketing still needs attribution, campaign performance and analytics. The point is to govern the infrastructure producing those insights with the same professionalism used elsewhere in a regulated enterprise.
The real weakness is between departments
The most interesting part of the bank example is not the number 48. It is that a sophisticated organization can achieve public marketing success while the infrastructure underneath that success remains distributed across Marketing, Technology, Legal, Privacy, Risk, Procurement and outside suppliers.
Marketing may approve the campaign without seeing the complete data map. Legal may approve the privacy language without inspecting the network sequence. Developers may implement specifications supplied by an agency, while the agency deploys familiar advertising technologies without visibility into the bank’s wider regulatory position.
Nobody needs to be careless for the combined result to be poorly governed.
“The browser does not care which department owns the problem. It executes the combined decisions of all of them.”
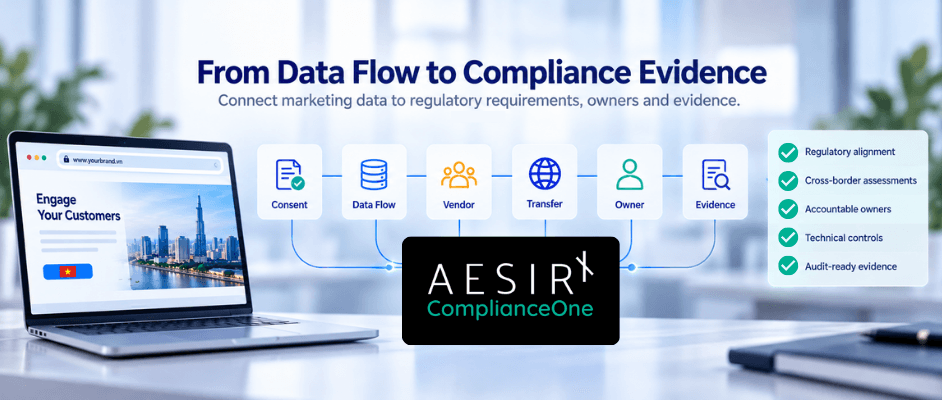
That is why privacy engineering and GRC need to meet in the same operating model. The organization needs one governed view linking regulatory requirements, processing activities, vendors, consent, transfers, technical controls, evidence and accountable owners.
Without that connection, every department can own part of compliance while nobody owns the complete proof.
What good governance would look like
Before a campaign launches, a regulated organization should already know the third-party technologies involved and the processing they create. Changes to tag managers, analytics, advertising pixels, embedded media or conversion infrastructure should pass through controlled review in the same way other regulated system changes do.
The evidence chain should be easy to reconstruct:
Regulatory requirement → processing activity → website/application → purpose → data categories → consent requirement and evidence → vendor/recipient → cross-border assessment → accountable owner → technical control → implementation test → ongoing monitoring.
When Marketing introduces a new supplier, the vendor and processing records change. When an agency introduces another tag, the technical inventory changes. When a new purpose is introduced, the consent configuration is reviewed. When a recipient or transfer route changes, the transfer assessment is updated. When the website changes in production, monitoring confirms whether the approved control is still the control that is actually running.
That is operational compliance. The evidence is created while the business operates rather than reconstructed after somebody asks for it.
The campaign deserved two success metrics
The marketing award recognized one form of excellence: the campaign achieved something valuable enough to receive external recognition.
There should be another measure of success for digital marketing in a regulated industry: whether the organization can prove that the data infrastructure behind the campaign was governed as professionally as the campaign itself.
Every material third-party flow should be known. Every purpose should have an owner. Consent should technically control the relevant processing where required. Cross-border activity should be assessed. Changes should be governed. Evidence should remain attributable after the campaign ends.
That does not diminish marketing innovation. It protects it.
A campaign whose commercial performance is measurable and whose regulatory operation is provable is stronger than one optimized only for conversion.
The browser is becoming part of the audit trail
For years, corporate privacy programmes concentrated heavily on documentation. Privacy notices, processor agreements, policies and assessment files remain necessary, but websites provide something else: externally observable technical behaviour.
If an organization states that tracking waits for consent, the implementation can be tested. If an obsolete provider is supposed to have been removed, its requests can be looked for. If data is supposed to remain within approved destinations, network traffic can show where the browser is actually communicating.
This creates a powerful accountability mechanism because a technical implementation is harder to reinterpret after the fact.
“Digital compliance becomes real when the policy, the consent record and the network traffic all tell the same story.”
For CMOs, DPOs, CIOs and boards, this should change the conversation before a campaign goes live. The question is not only how the campaign will perform, but how its data processing will be controlled, evidenced and reviewed.
From campaign measurement to operational proof
This is the problem we built AesirX ComplianceOne to address.
ComplianceOne provides the governance layer around the systems an organization already operates. It connects regulatory requirements to processing activities, consent purposes, data flows, vendors, assessments, accountable owners, remediation, evidence, approvals, incidents and audit history.
Combined with first-party consent and technical privacy controls, that creates a continuous chain from the regulatory requirement to the technical implementation. Marketing can continue measuring performance, agencies can continue building campaigns and digital teams can continue moving quickly, while Legal, Privacy, Risk and management gain visibility into the data infrastructure those activities create.
The goal is straightforward: know what is happening, control what is permitted to happen and retain the evidence showing what actually happened.
The next time a Vietnamese bank, insurer, retailer or digital platform wins a marketing award, I hope the campaign deserves the celebration. I will still be interested in one other result: what happened in the browser?
The trophy stays in the office. The data goes somewhere else.
Vietnam’s regulatory environment increasingly expects organizations to know exactly where.
Ronni K. Gothard Christiansen
Technical Privacy Engineer & CEO, AesirX.io
Laws and instruments referenced
- Personal Data Protection Law 91/2025/QH15 — issued 26 June 2025 and effective 1 January 2026; establishes Vietnam’s current statutory personal-data-protection framework.
- Decree 356/2025/NĐ-CP — issued 31 December 2025 and effective 1 January 2026; implements the PDPL and expressly lists behavioural tracking and specified financial/banking information among sensitive personal data.
- Decree 330/2026/NĐ-CP — issued and effective 19 August 2026; establishes the administrative-penalty framework for cybersecurity and personal-data protection. The maximum organizational penalty for violations of cross-border personal-data-transfer rules can reach 5% of prior-year revenue, with detailed revenue-based bands for specified serious violations.
- Data Law 60/2024/QH15 and Decree 165/2025/NĐ-CP — form the wider data-governance framework; Decree 165 has been effective since 1 July 2025.
- Decision 20/2025/QĐ-TTg — effective 1 July 2025; establishes Vietnam’s official lists of important and core data and is relevant to large-scale and sensitive data holdings.
Disclaimer
This article discusses technical observations and regulatory exposure from the perspective of a privacy-engineering and compliance-technology provider. The bank is intentionally not identified, and the observations described here are not an administrative or judicial finding of a violation. Actual legal characterization, applicability, data classification and penalties depend on the processing involved, the data categories, affected data subjects, recipients, transfer arrangements and findings of the competent authorities.
Organizations should obtain qualified legal advice before making regulatory filings, cross-border transfer assessments, data-classification decisions or enforcement-risk conclusions. AesirX ComplianceOne and Forseti support regulatory mapping, operational compliance workflows, evidence management and audit preparation, but do not replace qualified legal counsel or accountable human review and approval.


